Sigma rule: MSI Spawned Cmd and Powershell Spawned Processes
A detection rule from the SigmaHQ repository, shown as its author published it. Dataset version ref-78d35c1cea8f, updated 2020-10-13T00:00:00.000Z.
Rule
- Title
- MSI Spawned Cmd and Powershell Spawned Processes
- Status
- unsupported
- Level
- high
- Author
- Teymur Kheirkhabarov (idea), Mangatas Tondang (rule), oscd.community
- Date
- 2020/10/13
- File
- unsupported/windows/sysmon_always_install_elevated_msi_spawned_cmd_and_powershell_spawned_processes.yml
- Commit
- ccbb0369507f796db0b0ae6854c8a2be471b9d84
This rule looks for Windows Installer service (msiexec.exe) spawning command line and/or powershell that spawns other processes
Log source
- product
- windows
- category
- process_creation
- definition
- Works only if Enrich Sysmon events with additional information about process in ParentOfParentImage check enrichment section
Detection
parent_image:
    ParentImage|endswith:
        - '\cmd.exe'
        - '\powershell.exe'
parent_of_parent_image:
    ParentOfParentImage|contains|all:
        - '\Windows\Installer\'
        - 'msi'
    ParentOfParentImage|endswith:
        - 'tmp'
condition: parent_image and parent_of_parent_image
False positives (as the rule lists them)
- Unknown
Tags
- attack.privilege_escalation
- attack.t1548.002
MITRE ATT&CK ids this rule names
References
- https://image.slidesharecdn.com/kheirkhabarovoffzonefinal-181117201458/95/hunting-for-privilege-escalation-in-windows-environment-50-638.jpg
- https://www.slideshare.net/heirhabarov/hunting-for-privilege-escalation-in-windows-environment
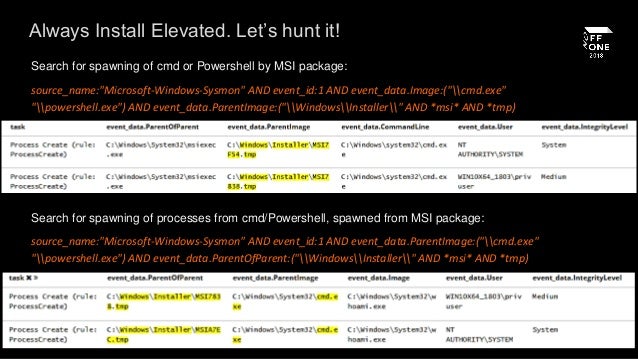
Read on 2026-11-03T00:58:21.399Z under licence sigma-drl-1.1@d5f4c36a from https://github.com/SigmaHQ/sigma/blob/ccbb0369507f796db0b0ae6854c8a2be471b9d84/unsupported/windows/sysmon_always_install_elevated_msi_spawned_cmd_and_powershell_spawned_processes.yml
Sources and licences
SigmaHQ
"MSI Spawned Cmd and Powershell Spawned Processes" by Teymur Kheirkhabarov (idea), Mangatas Tondang (rule), oscd.community (SigmaHQ). Rule: https://github.com/SigmaHQ/sigma/blob/ccbb0369507f796db0b0ae6854c8a2be471b9d84/unsupported/windows/sysmon_always_install_elevated_msi_spawned_cmd_and_powershell_spawned_processes.yml.
Licensed under the Detection Rule License (DRL) 1.1: https://github.com/SigmaHQ/Detection-Rule-License
Cite this page
Dragons Eye Ransomware Tracker, "Sigma rule: MSI Spawned Cmd and Powershell Spawned Processes",
entity page, dataset version ref-78d35c1cea8f, updated 2020-10-13T00:00:00.000Z,
https://ransomware-tracker.com/detections/sigma/38cf8340-461b-4857-bf99-23a41f772b18 (accessed 2026-11-03).
Underlying source: SigmaHQ rule 38cf8340-461b-4857-bf99-23a41f772b18, commit ccbb0369507f796db0b0ae6854c8a2be471b9d84.
Pages change. The dataset version identifies the data, but no archive of old versions is kept, so this citation cannot be replayed later.