Sigma rule: HackTool - Credential Dumping Tools Named Pipe Created
A detection rule from the SigmaHQ repository, shown as its author published it. Dataset version ref-59d7dfd5133a, updated 2023-08-07T00:00:00.000Z.
Rule
- Title
- HackTool - Credential Dumping Tools Named Pipe Created
- Status
- test
- Level
- critical
- Author
- Teymur Kheirkhabarov, oscd.community
- Date
- 2019-11-01
- Modified
- 2023-08-07
- File
- rules/windows/pipe_created/pipe_created_hktl_generic_cred_dump_tools_pipes.yml
- Commit
- ccbb0369507f796db0b0ae6854c8a2be471b9d84
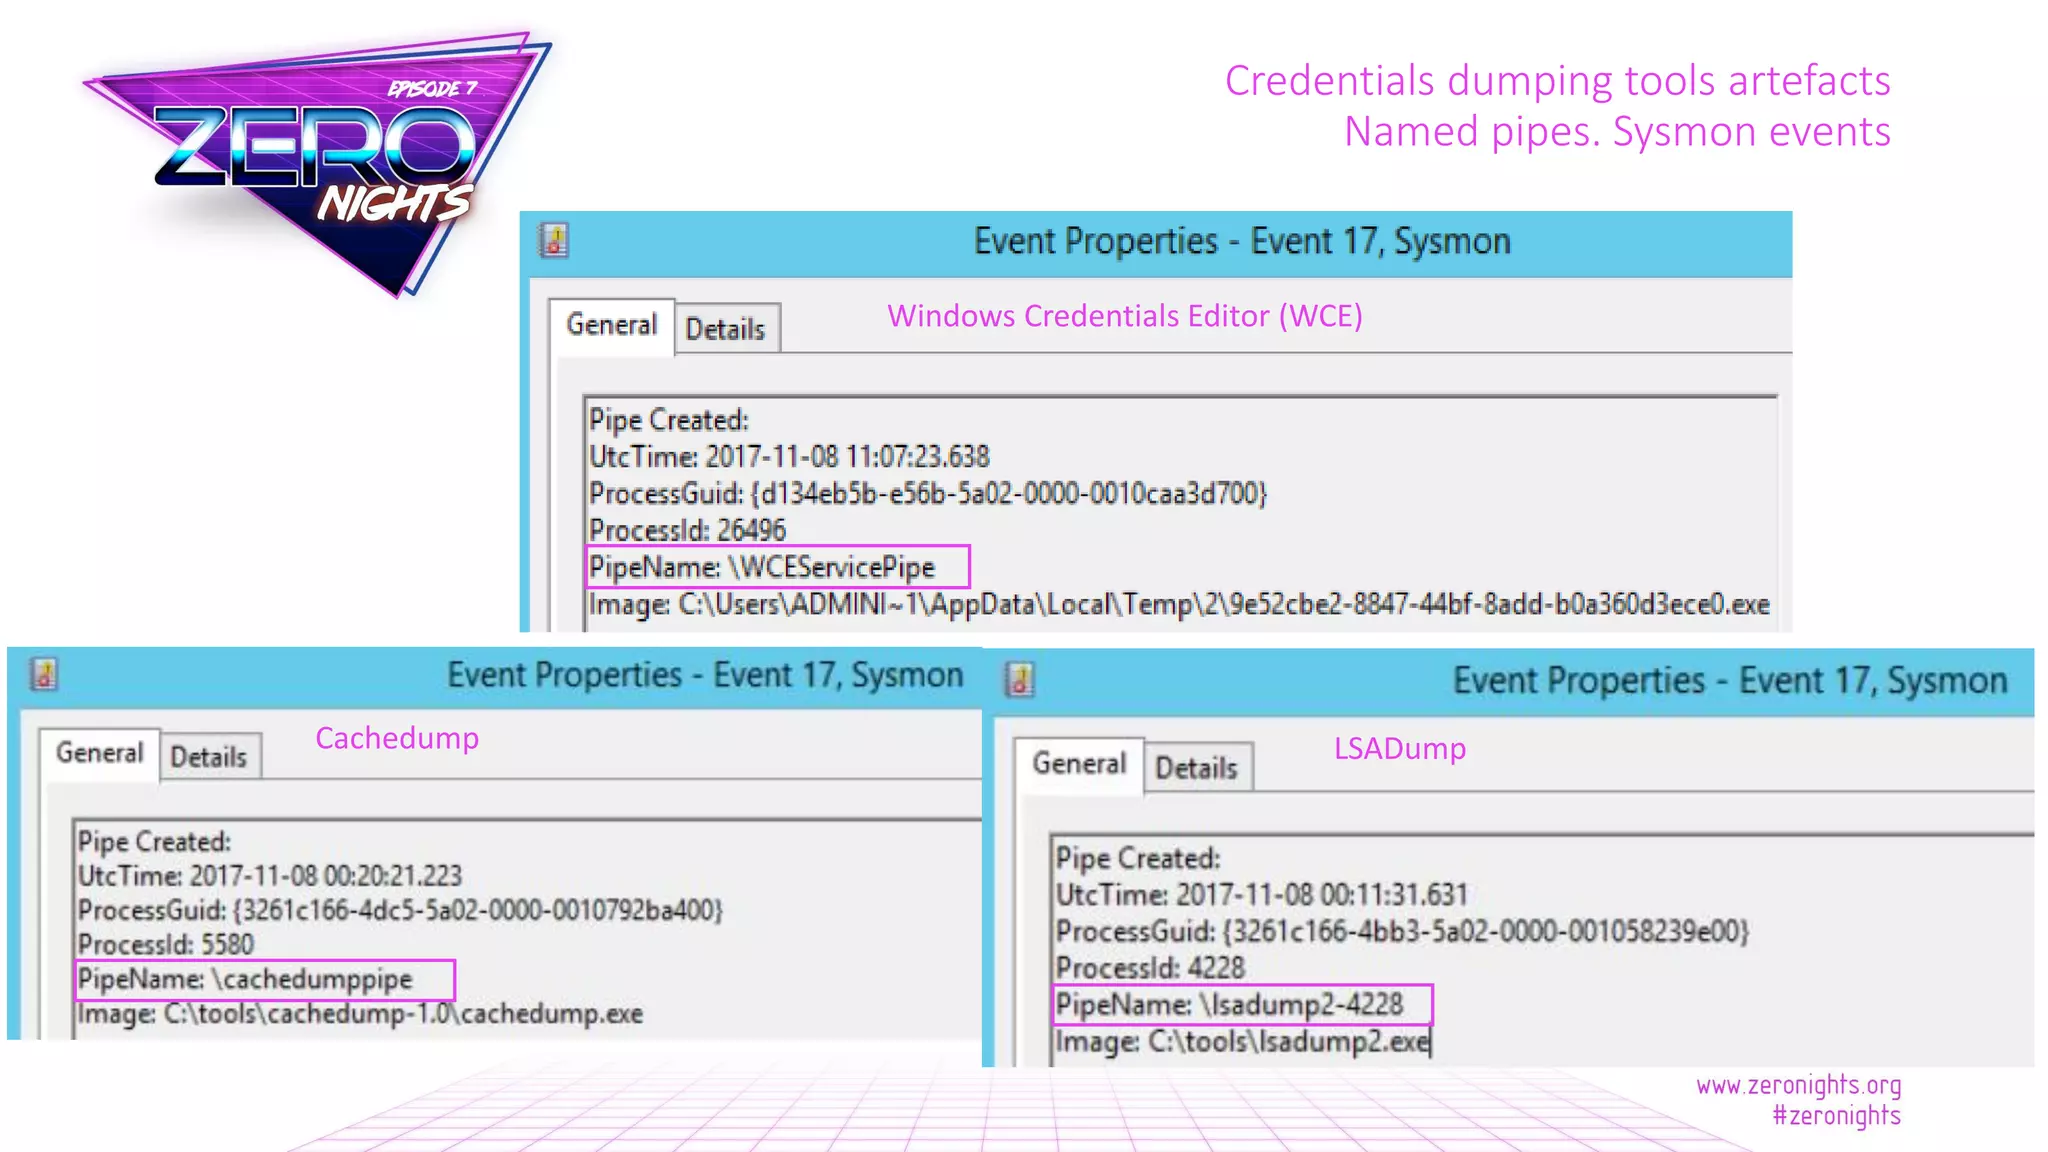
Detects well-known credential dumping tools execution via specific named pipe creation
Log source
- product
- windows
- category
- pipe_created
- definition
- Note that you have to configure logging for Named Pipe Events in Sysmon config (Event ID 17 and Event ID 18). The basic configuration is in popular sysmon configuration (https://github.com/SwiftOnSecurity/sysmon-config), but it is worth verifying. You can also use other repo, e.g. https://github.com/Neo23x0/sysmon-config, https://github.com/olafhartong/sysmon-modular. How to test detection? You can check powershell script from this site https://svch0st.medium.com/guide-to-named-pipes-and-hunting-for-cobalt-strike-pipes-dc46b2c5f575
Detection
selection:
    PipeName|contains:
        - '\cachedump'
        - '\lsadump'
        - '\wceservicepipe'
condition: selection
False positives (as the rule lists them)
- Legitimate Administrator using tool for password recovery
Tags
- attack.credential-access
- attack.t1003.001
- attack.t1003.002
- attack.t1003.004
- attack.t1003.005
MITRE ATT&CK ids this rule names
References
- https://www.slideshare.net/heirhabarov/hunting-for-credentials-dumping-in-windows-environment
- https://image.slidesharecdn.com/zeronights2017kheirkhabarov-171118103000/75/hunting-for-credentials-dumping-in-windows-environment-57-2048.jpg?cb=1666035799
Read on 2026-11-03T00:58:21.399Z under licence sigma-drl-1.1@d5f4c36a from https://github.com/SigmaHQ/sigma/blob/ccbb0369507f796db0b0ae6854c8a2be471b9d84/rules/windows/pipe_created/pipe_created_hktl_generic_cred_dump_tools_pipes.yml
Sources and licences
SigmaHQ
"HackTool - Credential Dumping Tools Named Pipe Created" by Teymur Kheirkhabarov, oscd.community (SigmaHQ). Rule: https://github.com/SigmaHQ/sigma/blob/ccbb0369507f796db0b0ae6854c8a2be471b9d84/rules/windows/pipe_created/pipe_created_hktl_generic_cred_dump_tools_pipes.yml.
Licensed under the Detection Rule License (DRL) 1.1: https://github.com/SigmaHQ/Detection-Rule-License
Cite this page
Dragons Eye Ransomware Tracker, "Sigma rule: HackTool - Credential Dumping Tools Named Pipe Created",
entity page, dataset version ref-59d7dfd5133a, updated 2023-08-07T00:00:00.000Z,
https://ransomware-tracker.com/detections/sigma/961d0ba2-3eea-4303-a930-2cf78bbfcc5e (accessed 2026-11-03).
Underlying source: SigmaHQ rule 961d0ba2-3eea-4303-a930-2cf78bbfcc5e, commit ccbb0369507f796db0b0ae6854c8a2be471b9d84.
Pages change. The dataset version identifies the data, but no archive of old versions is kept, so this citation cannot be replayed later.