Sigma rule: Suspicious WebDav Client Execution Via Rundll32.EXE
A detection rule from the SigmaHQ repository, shown as its author published it. Dataset version ref-734e179b60d9, updated 2023-09-18T00:00:00.000Z.
Rule
- Title
- Suspicious WebDav Client Execution Via Rundll32.EXE
- Status
- test
- Level
- high
- Author
- Nasreddine Bencherchali (Nextron Systems), Florian Roth (Nextron Systems)
- Date
- 2023-03-16
- Modified
- 2023-09-18
- File
- rules/windows/process_creation/proc_creation_win_rundll32_webdav_client_susp_execution.yml
- Commit
- ccbb0369507f796db0b0ae6854c8a2be471b9d84
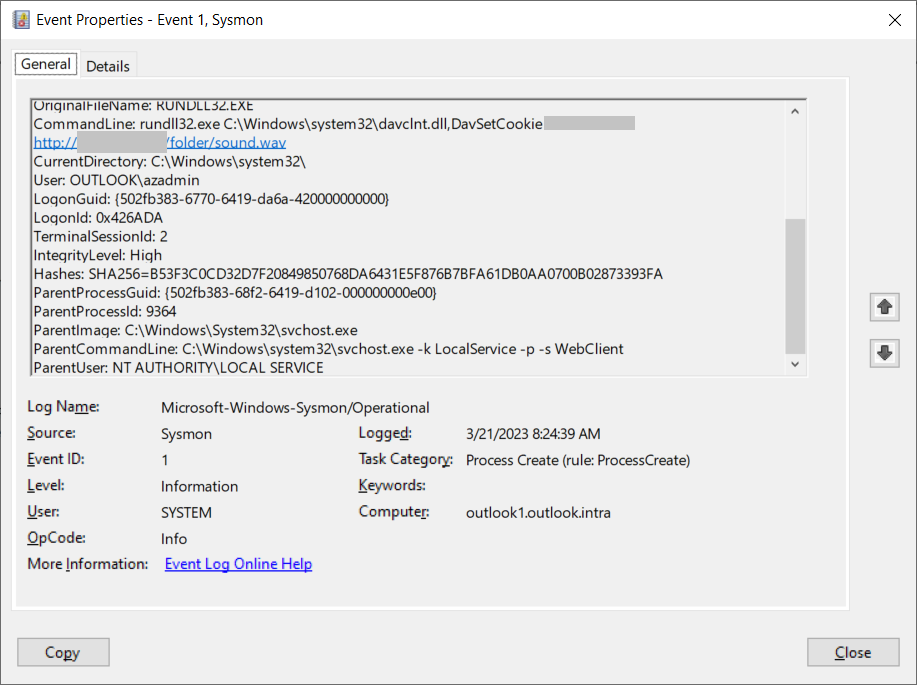
Detects "svchost.exe" spawning "rundll32.exe" with command arguments like C:\windows\system32\davclnt.dll,DavSetCookie. This could be an indicator of exfiltration or use of WebDav to launch code (hosted on WebDav Server) or potentially a sign of exploitation of CVE-2023-23397
Log source
- product
- windows
- category
- process_creation
Detection
selection:
    ParentImage|endswith: '\svchost.exe'
    ParentCommandLine|contains: '-s WebClient'
    Image|endswith: '\rundll32.exe'
    CommandLine|contains: 'C:\windows\system32\davclnt.dll,DavSetCookie'
    CommandLine|re: '://\d{1,3}\.\d{1,3}\.\d{1,3}\.\d{1,3}'
filter_local_ips:
    CommandLine|contains:
        - '://10.' # 10.0.0.0/8
        - '://192.168.' # 192.168.0.0/16
        - '://172.16.' # 172.16.0.0/12
        - '://172.17.'
        - '://172.18.'
        - '://172.19.'
        - '://172.20.'
        - '://172.21.'
        - '://172.22.'
        - '://172.23.'
        - '://172.24.'
        - '://172.25.'
        - '://172.26.'
        - '://172.27.'
        - '://172.28.'
        - '://172.29.'
        - '://172.30.'
        - '://172.31.'
        - '://127.' # 127.0.0.0/8
        - '://169.254.' # 169.254.0.0/16
condition: selection and not 1 of filter_*
False positives (as the rule lists them)
- Unknown
Tags
- attack.exfiltration
- attack.t1048.003
- cve.2023-23397
CVEs this rule names
MITRE ATT&CK ids this rule names
References
- https://twitter.com/aceresponder/status/1636116096506818562
- https://www.mdsec.co.uk/2023/03/exploiting-cve-2023-23397-microsoft-outlook-elevation-of-privilege-vulnerability/
- https://www.pwndefend.com/2023/03/15/the-long-game-persistent-hash-theft/
- https://www.microsoft.com/en-us/security/blog/wp-content/uploads/2023/03/Figure-7-sample-webdav-process-create-event.png
- https://www.microsoft.com/en-us/security/blog/2023/03/24/guidance-for-investigating-attacks-using-cve-2023-23397/
Read on 2026-11-03T00:58:21.399Z under licence sigma-drl-1.1@d5f4c36a from https://github.com/SigmaHQ/sigma/blob/ccbb0369507f796db0b0ae6854c8a2be471b9d84/rules/windows/process_creation/proc_creation_win_rundll32_webdav_client_susp_execution.yml
Sources and licences
SigmaHQ
"Suspicious WebDav Client Execution Via Rundll32.EXE" by Nasreddine Bencherchali (Nextron Systems), Florian Roth (Nextron Systems) (SigmaHQ). Rule: https://github.com/SigmaHQ/sigma/blob/ccbb0369507f796db0b0ae6854c8a2be471b9d84/rules/windows/process_creation/proc_creation_win_rundll32_webdav_client_susp_execution.yml.
Licensed under the Detection Rule License (DRL) 1.1: https://github.com/SigmaHQ/Detection-Rule-License
Cite this page
Dragons Eye Ransomware Tracker, "Sigma rule: Suspicious WebDav Client Execution Via Rundll32.EXE",
entity page, dataset version ref-734e179b60d9, updated 2023-09-18T00:00:00.000Z,
https://ransomware-tracker.com/detections/sigma/982e9f2d-1a85-4d5b-aea4-31f5e97c6555 (accessed 2026-11-03).
Underlying source: SigmaHQ rule 982e9f2d-1a85-4d5b-aea4-31f5e97c6555, commit ccbb0369507f796db0b0ae6854c8a2be471b9d84.
Pages change. The dataset version identifies the data, but no archive of old versions is kept, so this citation cannot be replayed later.