Sigma rule: Abused Debug Privilege by Arbitrary Parent Processes
A detection rule from the SigmaHQ repository, shown as its author published it. Dataset version ref-8933f2c8523f, updated 2022-11-11T00:00:00.000Z.
Rule
- Title
- Abused Debug Privilege by Arbitrary Parent Processes
- Status
- test
- Level
- high
- Author
- Semanur Guneysu @semanurtg, oscd.community
- Date
- 2020-10-28
- Modified
- 2022-11-11
- File
- rules/windows/process_creation/proc_creation_win_susp_abusing_debug_privilege.yml
- Commit
- ccbb0369507f796db0b0ae6854c8a2be471b9d84
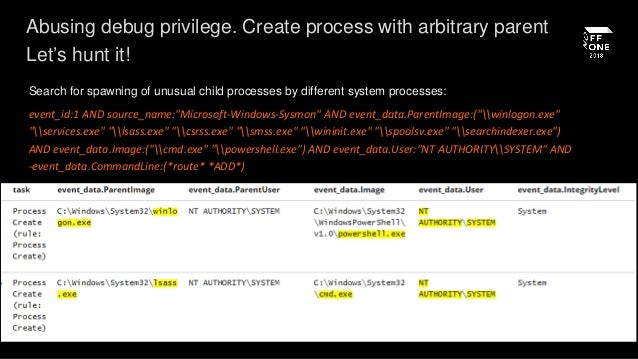
Detection of unusual child processes by different system processes
Log source
- product
- windows
- category
- process_creation
Detection
selection_parent:
    ParentImage|endswith:
        - '\winlogon.exe'
        - '\services.exe'
        - '\lsass.exe'
        - '\csrss.exe'
        - '\smss.exe'
        - '\wininit.exe'
        - '\spoolsv.exe'
        - '\searchindexer.exe'
    User|contains: # covers many language settings
        - 'AUTHORI'
        - 'AUTORI'
selection_img:
    - Image|endswith:
          - '\powershell.exe'
          - '\pwsh.exe'
          - '\cmd.exe'
    - OriginalFileName:
          - 'PowerShell.EXE'
          - 'pwsh.dll'
          - 'Cmd.Exe'
filter:
    CommandLine|contains|all:
        - ' route '
        - ' ADD '
condition: all of selection_* and not filter
False positives (as the rule lists them)
- Unknown
Tags
- attack.privilege-escalation
- attack.t1548
MITRE ATT&CK ids this rule names
References
Read on 2026-11-03T00:58:21.399Z under licence sigma-drl-1.1@d5f4c36a from https://github.com/SigmaHQ/sigma/blob/ccbb0369507f796db0b0ae6854c8a2be471b9d84/rules/windows/process_creation/proc_creation_win_susp_abusing_debug_privilege.yml
Sources and licences
SigmaHQ
"Abused Debug Privilege by Arbitrary Parent Processes" by Semanur Guneysu @semanurtg, oscd.community (SigmaHQ). Rule: https://github.com/SigmaHQ/sigma/blob/ccbb0369507f796db0b0ae6854c8a2be471b9d84/rules/windows/process_creation/proc_creation_win_susp_abusing_debug_privilege.yml.
Licensed under the Detection Rule License (DRL) 1.1: https://github.com/SigmaHQ/Detection-Rule-License
Cite this page
Dragons Eye Ransomware Tracker, "Sigma rule: Abused Debug Privilege by Arbitrary Parent Processes",
entity page, dataset version ref-8933f2c8523f, updated 2022-11-11T00:00:00.000Z,
https://ransomware-tracker.com/detections/sigma/d522eca2-2973-4391-a3e0-ef0374321dae (accessed 2026-11-03).
Underlying source: SigmaHQ rule d522eca2-2973-4391-a3e0-ef0374321dae, commit ccbb0369507f796db0b0ae6854c8a2be471b9d84.
Pages change. The dataset version identifies the data, but no archive of old versions is kept, so this citation cannot be replayed later.